
Hi Buddy, in this blog plus article I want to explain how to exploit port 25/tcp open smtp Postfix smtpd in a metasploitable vulnerable machine in a virtual box version 1, 2 and 3 and this technique supports all future versions also.
Before exploitation we need to understand what is port 25 and what is smtp (Simple Mail Transfer Protocol).
Do you know how we are able to send E-Mail using Gmail or any other mail service?
If you know then you are able Understand what is Simple Mail Transfer Protocol is.
With-out this protocol we are not able to send any mail.
This Exploitation is divided into multiple steps if any step you already done so just skip and jump to the next step.
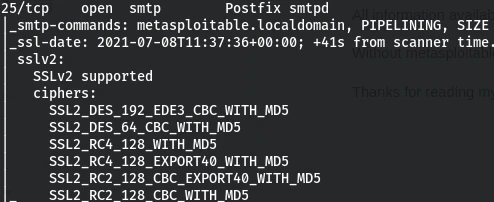
Step 1 Nmap Port 25 Scan
nmap -T4 -A -p 80 Run this command if you don’t know the meaning see below i will explain.
nmap -T4 -A -p 25 198.xxx.xx.xxx
- -T4 for (-T<0-5>: Set timing (higher is faster)
- -A for (-A: Enable OS detection, version detection, script scanning, and traceroute)
- -p 25 for ( -p : Only scan 25 ports or SMTP)
- 198.xxx.xx.xxx (Host IP Address or Host name)
┌──(kali㉿kali)-[~/vm/metaspoitable_vm]
└─$ nmap -T4 -A -p 25 192.xxx.xx.xxx
Starting Nmap 7.92 ( https://nmap.org ) at 2021-12-14 16:34 IST
Nmap scan report for meta.meta (192.xxx.xx.xxx)
Host is up (0.021s latency).

PORT   STATE SERVICE VERSION
25/tcp open  smtp    Postfix smtpd
| ssl-cert: Subject: commonName=ubuntu804-base.localdomain/organizationName=OCOSA/stateOrProvinceName=There is no such thing outside US/countryName=XX
| Not valid before: 2010-03-17T14:07:45
|_Not valid after:  2010-04-16T14:07:45
|_smtp-commands: metasploitable.localdomain, PIPELINING, SIZE 10240000, VRFY, ETRN, STARTTLS, ENHANCEDSTATUSCODES, 8BITMIME, DSN
| sslv2:
|   SSLv2 supported
|   ciphers:
|     SSL2_RC4_128_EXPORT40_WITH_MD5
|     SSL2_DES_64_CBC_WITH_MD5
|     SSL2_RC4_128_WITH_MD5
|     SSL2_RC2_128_CBC_WITH_MD5
|     SSL2_RC2_128_CBC_EXPORT40_WITH_MD5
|_    SSL2_DES_192_EDE3_CBC_WITH_MD5
|_ssl-date: 2021-12-14T11:05:24+00:00; +1m20s from scanner time.
Service Info: Host:  metasploitable.localdomain

Host script results:
|_clock-skew: 1m19s

Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
Nmap done: 1 IP address (1 host up) scanned in 2.57 seconds
Result:-
Port 25 open with SMTP in Linux Operating System and Postfix mail server version.
Smtp commands: metasploitable.localdomain, PIPELINING, SIZE 10240000, VRFY, ETRN, STARTTLS, ENHANCEDSTATUSCODES, 8BITMIME, DSN
And VRFY is a valid Command.
At this point we need to do more enumeration.
Step 2 SMTP Enumerate With Nmap
Nmap has so many scripts for Simple Mail Transfer Protocol enumeration.
I don’t want to waste your time But you still interested for all SMTP enu scripts then then visit nmap.org.
I just want to show you some important scripts so you have a better Idea how this works.
Run below command.
nmap --script smtp-enum-users.nse --script-args smtp-enum-users.methods={VREY} -p 25 192.xxx.xx.xxxResult:-
┌──(kali㉿kali)-[~/vm/metaspoitable_vm]
└─$ nmap --script smtp-enum-users.nse --script-args smtp-enum-users.methods={VREY} -p 25 192.xxx.xx.xxx
Starting Nmap 7.92 ( https://nmap.org ) at 2021-12-14 17:01 IST
Nmap scan report for meta.meta (192.xxx.xx.xxx)
Host is up (0.0096s latency).

PORT   STATE SERVICE
25/tcp open  smtp
| smtp-enum-users:
|_  Invalid method found, VREY

Nmap done: 1 IP address (1 host up) scanned in 0.92 seconds
Run Below command for CVE 2010-4344
nmap --script smtp-vuln-cve2010-4344 -p25 192.XXX.XX.XXX
Result:-
┌──(kali㉿kali)-[~/vm/metaspoitable_vm]
└─$ nmap --script smtp-vuln-cve2010-4344 -p25 192.xxx.xx.xxx                                                                                                        1 ⨯
Starting Nmap 7.92 ( https://nmap.org ) at 2021-12-14 17:08 IST
Nmap scan report for meta.meta (192.xxx.xx.xxx)
Host is up (0.00063s latency).

PORT   STATE SERVICE
25/tcp open  smtp
| smtp-vuln-cve2010-4344:
|_  The SMTP server is not Exim: NOT VULNERABLE

Nmap done: 1 IP address (1 host up) scanned in 6.07 seconds
Now we are able to understand how to use nmap for smtp enumeration.
Step 3 Use smtp-user-enum Tool
All Linux testing OS already have smtp-user-enum Tool but for some reason you don’t have smtp-user-enum Tool then you have a question.
How to install smtp-user-enum ro smtp user enum Tool in Linux Terminal?
Just run below two commands in Linux Terminal.
sudo apt update
sudo apt install smtp-user-enum
Know you have smtp-tool then run below command for port 25.
smtp-user-enum -M VRFY -U /usr/share/metasploit-framework/data/wordlists/unix_users.txt -t 192.xxx.xx.xxxMaybe you have a question: what is the meaning of this command?
- Smtp-user-enum: Tool Name
- -M VRFY: Method to use for username guessing EXPN, VRFY or RCPT (default: VRFY)
- -U : File of usernames to check via smtp service
- -t : Server host running smtp service
Run this command see result below.
┌──(kali㉿kali)-[~/vm/metaspoitable_vm]
└─$ smtp-user-enum  -M VRFY -U /usr/share/metasploit-framework/data/wordlists/unix_users.txt -t 192.xxx.xx.xxx
Starting smtp-user-enum v1.2 ( http://pentestmonkey.net/tools/smtp-user-enum )

 ----------------------------------------------------------
|                   Scan Information                       |
 ----------------------------------------------------------

Mode ..................... VRFY
Worker Processes ......... 5
Usernames file ........... /usr/share/metasploit-framework/data/wordlists/unix_users.txt
Target count ............. 1
Username count ........... 168
Target TCP port .......... 25
Query timeout ............ 5 secs
Target domain ............

######## Scan started at Tue Dec 14 16:49:10 2021 #########
192.xxx.xx.xxx: backup exists
192.xxx.xx.xxx: bin exists
192.xxx.xx.xxx: daemon exists
192.xxx.xx.xxx: distccd exists
192.xxx.xx.xxx: games exists
192.xxx.xx.xxx: ftp exists
192.xxx.xx.xxx: gnats exists
192.xxx.xx.xxx: irc exists
192.xxx.xx.xxx: list exists
192.xxx.xx.xxx: libuuid exists
192.xxx.xx.xxx: lp exists
192.xxx.xx.xxx: mail exists
192.xxx.xx.xxx: man exists
192.xxx.xx.xxx: mysql exists
192.xxx.xx.xxx: news exists
192.xxx.xx.xxx: nobody exists
192.xxx.xx.xxx: postmaster exists
192.xxx.xx.xxx: postgres exists
192.xxx.xx.xxx: proxy exists
192.xxx.xx.xxx: postfix exists
192.xxx.xx.xxx: ROOT exists
192.xxx.xx.xxx: root exists
192.xxx.xx.xxx: service exists
192.xxx.xx.xxx: sshd exists
192.xxx.xx.xxx: sync exists
192.xxx.xx.xxx: sys exists
192.xxx.xx.xxx: syslog exists
192.xxx.xx.xxx: user exists
192.xxx.xx.xxx: uucp exists
192.xxx.xx.xxx: www-data exists
######## Scan completed at Tue Dec 14 16:49:11 2021 #########
30 results.

168 queries in 1 seconds (168.0 queries / sec)
Know you have a valid user list with only one step reaming.
Step 4 Install ssmtp Tool And Send Mail
Using the ssmtp tool you can send mail for any one target host to target mail id.
But as Cyber Security analysis or Pen Testers we don’t have to right do this.
If you find this type of exploitation in your server then immediately report to the Server Admin.
To avoid any invalid activity.
But we need to know how ssmtp tools work so i will recommend play with ssmtp tools on your Linux machine.
Conclusion
Nmap and Smtp-user-enum tools are able to enumerate the Simple Mail Transfer Protocol server but you have knowledge about the correct command.
All information available in your Linux OS just needs to figure out the correct pathway.
Without metasploitable vulnerable machines I am not able to share this information with you.
Thanks for reading my article.
Other Metasploitable Vulnerable Machine Article:-
How to Exploit Port 23?
How to Exploit Port 80?
How to Exploit Port 139 and 445?
How to Exploit Port 512, 513 and 514?
How to Exploit Port 1099?
How to Exploit Port 5900?